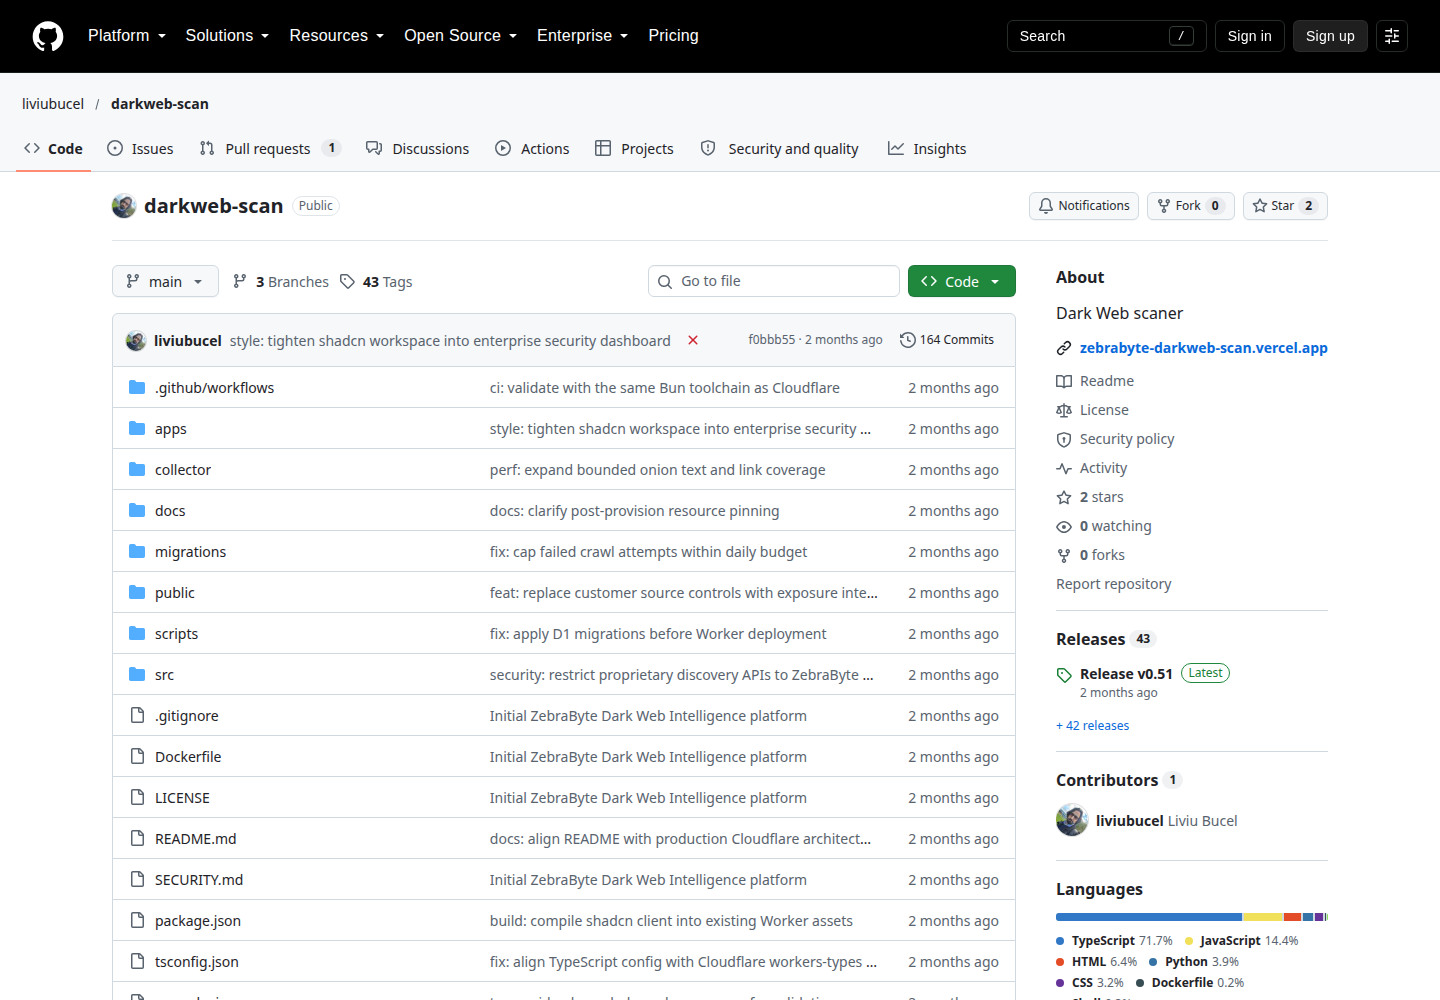
Code and demonstration
Problem to solve
An exposure-monitoring platform needs more than a search box: investigation state, isolated evidence, tenant access controls and defensible monitoring workflows.
Architecture and approach
The public implementation uses Cloudflare Workers for the application/API; Workflows and Queues for orchestrated investigations; D1 for structured state; R2 for retained evidence; and Workers AI for constrained defensive analysis. A short-lived Tor collector is isolated in a Cloudflare Container.
What it provides
Tenant-scoped investigations, monitoring jobs, quotas and audit metadata Cloudflare-native evidence retention and asynchronous processing Separate clear-web enrichment, private collection and AI-assisted analysis
Security considerations
Tor retrieval is constrained to validated .onion addresses; no generic proxy or internal-network scanner. Evidence is treated as untrusted input; service credentials do not belong in the collector. Optional features require provisioning; the public README explicitly distinguishes them from configured functionality.