Code and demonstration
Problem to solve
Manually issuing and renewing TLS certificates can introduce operational mistakes and expired certificates.
Architecture and approach
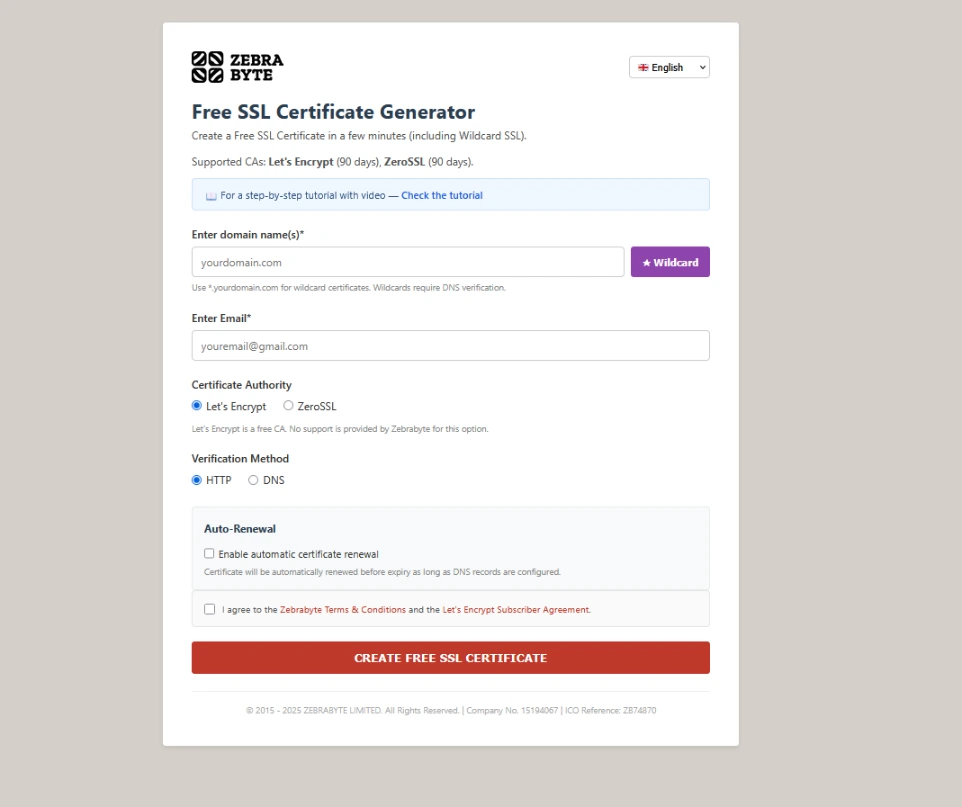
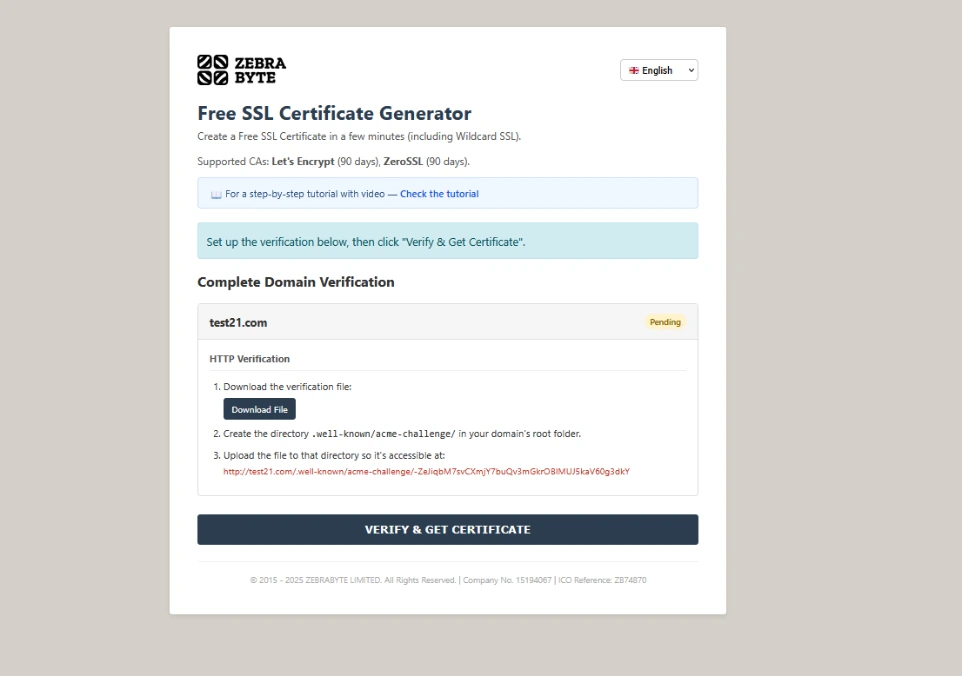
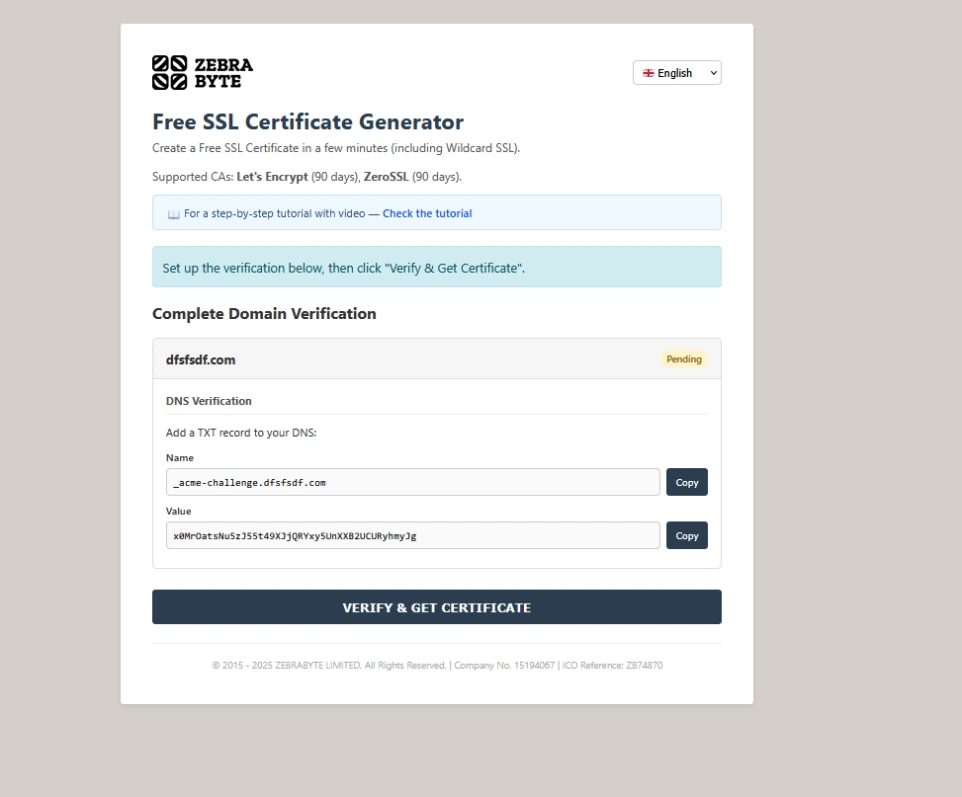
The open-source generator implements ACME workflows in a Cloudflare Worker. ZeroSSL is accessed directly; Let’s Encrypt requests can pass through a restricted Railway ACME proxy. The project documents HTTP-01/DNS-01 validation, wildcard certificates and renewal scheduling.
What it provides
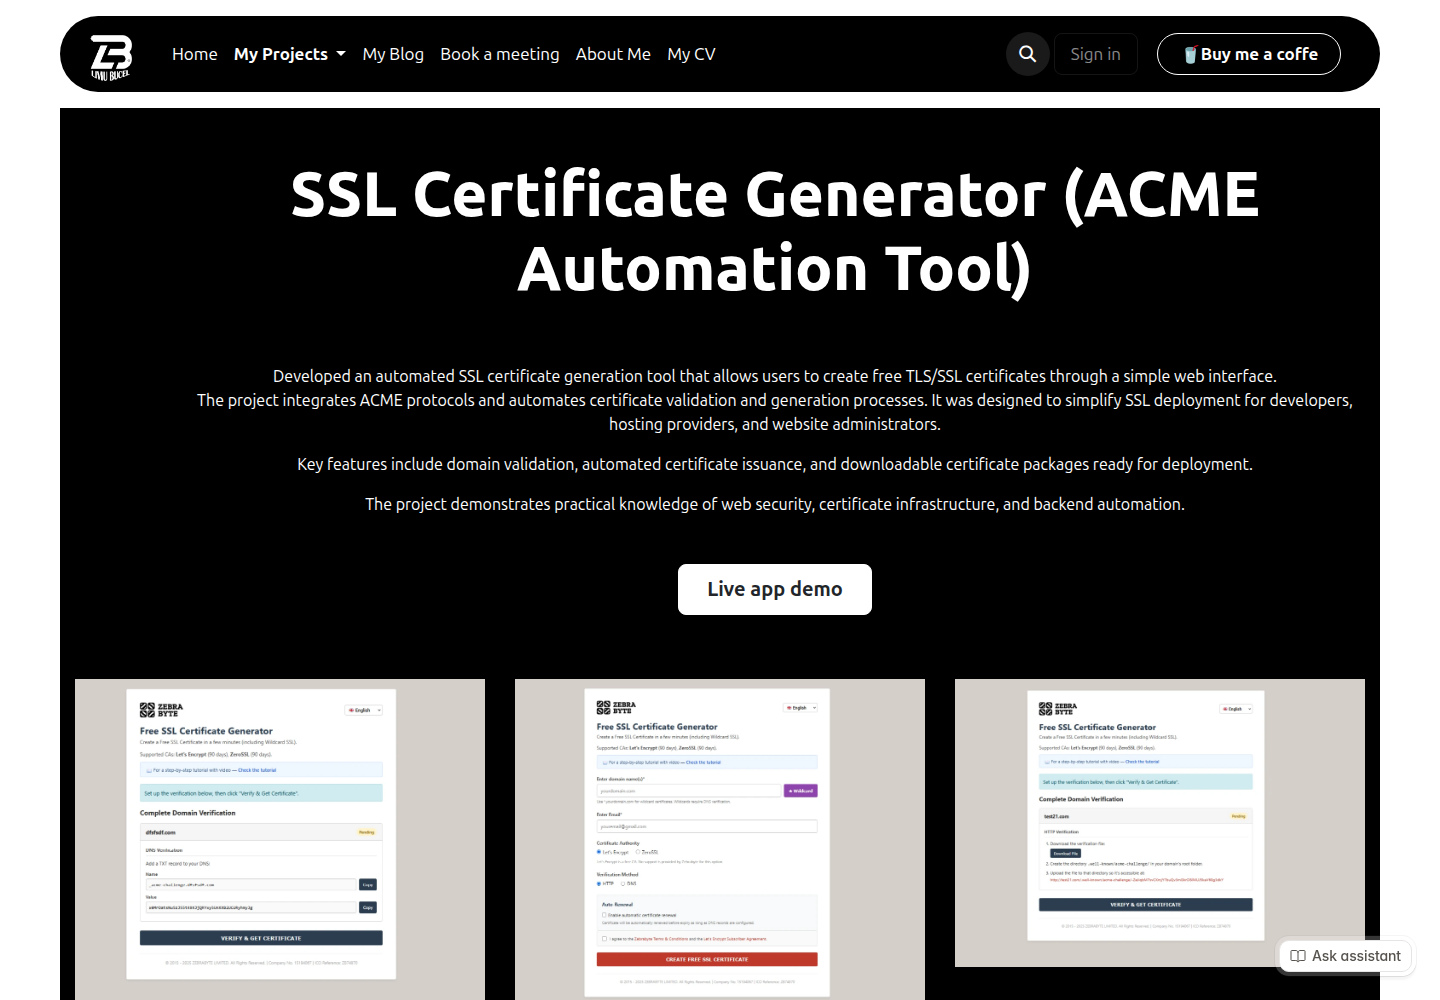
Certificate-issuance UI in English and Romanian Support for Let’s Encrypt and ZeroSSL, DNS-01 wildcard validation and downloadable certificate bundles Cloudflare KV for certificate state and renewal schedules; optional email notifications
Security considerations
CA credentials and renewal tokens are configured as secrets, never bundled in a public front-end. The proxy restricts CA destinations and uses a shared authentication token. The live demo can block automated access; the screenshot here is from the actual open-source repository, not a simulated certificate.